ISO 27701 Certification
Privacy Program Designed in Alignment with ISO 27701
Your enterprise customers want proof you handle their data responsibly. ISO 27701 certification gives you that proof. Decrypt Compliance’s CIPP/E-credentialed auditors conduct the audit and issue the certificate directly.
What Is a ISO 27701 Certification?
It establishes what’s called a Privacy Information Management System, or PIMS, a structured set of controls that govern how your organization collects, stores, uses, and shares personal data. It defines who is responsible for privacy decisions, how data subject requests get handled, how third-party processors are managed, and what happens when something goes wrong.
Note: The 2025 revision of ISO 27701 made it a standalone standard, meaning it can now be certified independently without requiring ISO 27001 first.
PII Controller
Your organization decides what personal data is collected and why; applies if you’re defining the purpose and means of processing customer or end-user data.
PII Processor
Who Needs ISO 27701 Certification?
ISO 27701 certification gives procurement teams, data protection officers, and legal counterparts a recognized framework to review. It keeps deals moving when vendor security reviews start asking about how you handle personal data.
- SaaS companies entering European markets
- API providers and data processors
- AI companies processing personal, behavioral, or biometric data
- Companies already holding ISO 27001
- Companies closing enterprise deals
Why Choose Decrypt Compliance For ISO 27701 Certification
Privacy-credentialed auditors, not generalists covering privacy
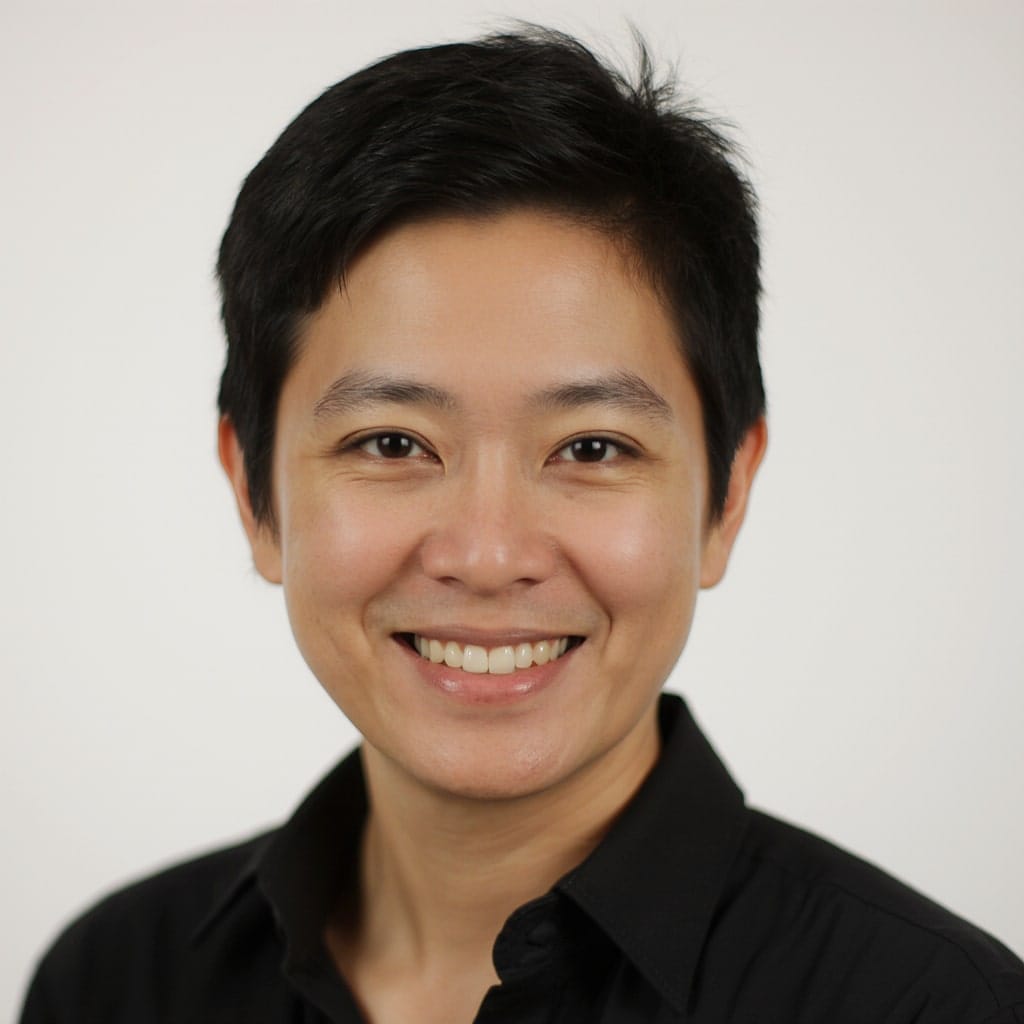
Raymond Cheng holds the CIPP/E, the leading credential for privacy professionals managing data protection under GDPR and related frameworks, alongside CISSP, CISA, and ISO 27001 Lead Auditor certifications.
Accredited to issue the certificate - not just advise on it
Decrypt Compliance is a registered ISO certification body. We conduct the audit and sign the certificate ourselves. There’s no separate firm involved at the end of the process. One engagement, one report, one relationship.
Founder-led and independent
Decrypt Compliance is privately held and founder-run – not PE-backed, no corporate parent setting utilization targets. That means the same senior auditors on your initial certification are on your annual surveillance audits in years two and three. No handoffs to junior staff, no re-explaining your setup every cycle.
Works with your existing GRC tools
Whether you’re using Vanta, Drata, or another compliance platform, Decrypt Compliance works alongside your tooling. What you’ve already built counts toward the audit.
Our Reviews
Client Stories

Ralph Hofacker
Co-Founder Brick Towers AG
Expectation for an expected timeline was given and also adhered to which helped us a lot to manage expectations with our prospects. Decrypt accommodated our additional input to the draft audit report which helped us to stand out.

Lior Romano
CEO, Tillion.ai

Kabir Mathur
CEO, Leen Inc
Eran R.
CEO · jumbomail.me

Zsolt B.
Mid-Market
Steven F.
Small Business

Alexandre C.
Small Business · France
Our Latest Articles
Cybersecurity Resources and Insights from Decrypt Compliance Experts


Frequently Asked Questions
ISO 27001 covers your overall information security management system. ISO 27701 covers privacy specifically - how your organization handles personally identifiable information. If you only have ISO 27001, your security posture is audited but your privacy program isn't independently verified. They address different buyer and regulatory concerns, and increasingly enterprise contracts require both.
Yes - the 2025 revision made ISO 27701 a standalone standard, so ISO 27001 is no longer a hard prerequisite. That said, if you have neither, pursuing both together is usually more efficient. The documentation and control work overlaps significantly, and a combined engagement avoids duplicating scoping and audit effort. We'll walk you through the tradeoffs during the scoping call.
Most engagements run two to four months from kickoff to certificate issuance. The main variables are how mature your existing privacy controls are and whether you're pursuing it alongside ISO 27001. We give you a realistic timeline during the scoping call based on your actual current state - not a best-case scenario.
That's common. The Stage 1 audit reviews your documentation and identifies gaps before we move into the implementation assessment. Any nonconformances found in Stage 2 go through a resolution process before certification is issued. We tell you exactly what needs to be addressed and work with you through it.
Significantly, yes. ISO 27701 maps directly to both GDPR and CCPA requirements at the control level. In practice, most organizations that have gone through a serious GDPR implementation have satisfied a substantial portion of the PIMS requirements. During scoping we review what you have so you're not rebuilding work you've already completed - and so we can give you an accurate picture of the remaining gap before you commit to the engagement.
Get Started
Ready to Get Certified and Close More Deals?
Tell us about your company and we’ll get back to you with a clear path to certification – including timeline and pricing.
- Submit the form and we'll reach out within one business day
- We'll book a short discovery call to understand your environment and goals
- You'll receive a fixed-fee quote with a clear timeline and next steps