SOC Auditors for B2B SaaS Companies
- AICPA peer-reviewed
- Founder-led, independent, no handoffs
- We guide and educate you
SOC Consulting & Audit Services
The Audit Partner That Guides You
For B2B SaaS companies, compliance isn’t optional. Enterprise buyers require it. Investors expect it. And the longer it takes, the more deals sit in limbo.
Decrypt Compliance works with you through every step – educating your team, adapting to your processes, and signing the report your customers actually need. No readiness consultants. No handoffs. Just one firm that takes you from kickoff to certified.
our services
Every Certification Your Customers Will Ever Ask For
SOC 1 Type I & II
SOC 2 Type I & II
SOC 3
ISO 27001
ISO 27701
ISO 42001
PCI DSS
HIPAA
HITRUST
GDPR
Non-compliance carries fines up to 4% of global revenue – we help you get and stay compliant.
How we do it
Compliance Journey
READINESS
Gap Assessment
Client and compliance team jointly identify gaps in the existing security program, define risk priorities, and map improvement targets before any controls work begins.
Implement Controls & Documentation
Client implements all required security controls and finalises supporting documentation prior to the official start of the Attestation Period.
Operate Controls
Client consistently operates all defined controls throughout the full Attestation Period, building the evidence trail auditors will review.
AUDIT
Auditor Testing Period
Compliance auditors actively test each control during the Attestation Period, verifying operating effectiveness through evidence review and walkthroughs.
Auditor Evaluation & Report
Compliance team reviews all testing results, resolves any exceptions, and drafts the formal certification report for client review and sign-off.
Final Report & Certification
Compliance team issues the final signed security certification report — completing the full audit lifecycle and confirming your compliance status.
Why Choose Us
Why Choose Decrypt Compliance for Your Audit and Certification Needs
Founder-Led, Not Investor-Led
Decrypt Compliance is independent. No PE ownership, no corporate parent, no pressure to scale at the expense of your audit. You work with a firm that answers to its clients.
AICPA Peer-Reviewed
Big 4 Trained, SaaS Focused
We Guide You, Not Just Audit You
Most auditors hand you a checklist and wait. We work with you through every step – explaining requirements, adapting to your processes, and making sure your team understands the outcome.
Same Team, Every Engagement
Awards & Recognition
Raymond Cheng Founder & CEO
AICPA Tech Advisory Standing Ovation Recognition (2024)
Named as one of Forbes'
America’s Best-In-State CPAs for 2025 & 2026
Raymond Cheng holds 7 certifications
CPA.CITP, CISSP, CISA, CCSK, CIPP/E, ISO 27001 Lead Auditor, ISO 42001 Lead Auditor
Our Reviews
Client Stories

Ralph Hofacker
Co-Founder Brick Towers AG
Expectation for an expected timeline was given and also adhered to which helped us a lot to manage expectations with our prospects. Decrypt Compliance accommodated our additional input to the draft audit report which helped us to stand out.

Lior Romano
CEO, Tillion.ai
The Decrypt Compliance team truly delivered on their promises. They kept us constantly updated to ensure no surprises, while also making it easy to enable a quality audit. Decrypt’s responsiveness and high standards kept me confident throughout the process.

Kabir Mathur
CEO, Leen Inc
Becoming SOC2 compliant was very important to us since we’re selling to other security companies. Decypt ran an efficient process to help us become compliant and close new deals.

Eran R.
CEO · jumbomail.me

Zsolt B.
Mid-Market
Steven F.
Small Business

Alexandre C.
Small Business · France
SOC 2 Compliance fit for all cloud-native products
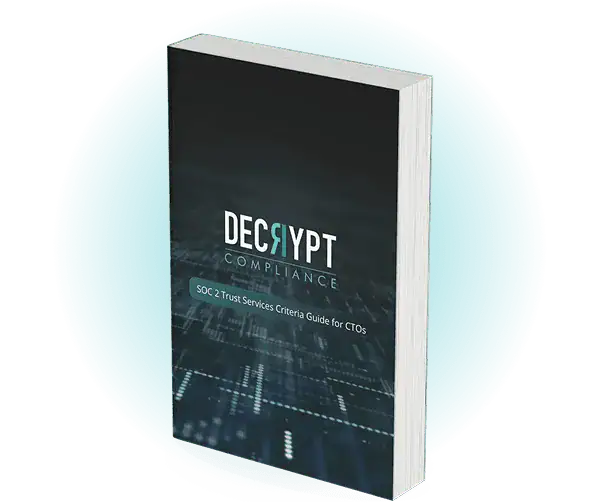
Learn About SOC 2 Trust Services Criteria from Decrypt Compliance’s Experts
Get the SOC 2 TSC guide for CTOs. Learn and get ahead of your competitors and ace your SOC 2 audit fast.
Reviewed by Holbrook & Manter, CPAs
AICPA Peer Review Rating
Our Latest Articles
Cybersecurity Resources and Insights from Decrypt Compliance Experts


Our Videos
The Auditor's Take on Compliance
Why did you start Decrypt Compliance?
Will a SOC 2 audit be worth the cost for my company?
What are the benefits of an independent compliance audit?
Frequently Asked Questions
Type I is a point-in-time report confirming your security controls are designed correctly. Type II covers an observation period - typically 6 to 12 months - and confirms that those controls are actually working. Most enterprise buyers require Type II before signing a contract.
Vanta and Drata are software tools that help you collect and organize evidence. They don't perform audits or issue reports. Decrypt is a licensed CPA firm - we conduct the audit, sign the report, and issue the certification your customers are asking for. If you're already using Vanta or Drata, we work alongside them.
A Type I audit typically takes 4 to 6 weeks. A Type II audit requires a minimum 6-month observation period, though the active audit work is much shorter. Our clients get certified 50% faster on average - we keep the process moving so your deals don't sit in limbo.
Yes. Many clients pursue SOC 2 alongside ISO 27001 or other frameworks. Because the same team handles every engagement, evidence collected for one audit can often carry over to others - cutting duplicate work and time.
It's more common than you'd think. The biggest complaints we hear are auditor turnover, lack of communication, and junior staff who don't understand SaaS products. We work differently - same team every engagement, senior-level auditors, and clear communication throughout.
It depends on the scope and complexity of your environment. What we can tell you upfront is that we use fixed-fee pricing - no hourly billing, no surprise invoices mid-engagement. Book a discovery call today.
Get Started
Ready to Get Certified and Close More Deals?
Tell us about your company and we’ll get back to you with a clear path to certification – including timeline and pricing.
- Submit the form and we'll reach out within one business day
- We'll book a short discovery call to understand your environment and goals
- You'll receive a fixed-fee quote with a clear timeline and next steps