Raymond Cheng, Founder and CEO of Decrypt Compliance, named as one of Forbes’ Best In-State CPA for 2026
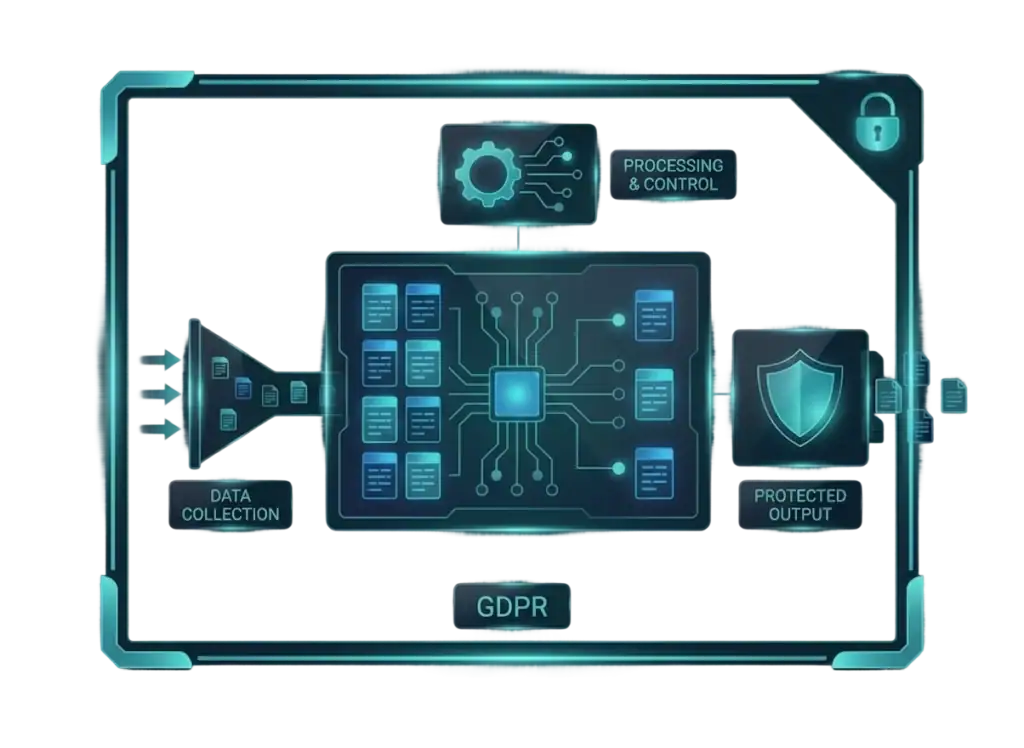
GDPR, the General Data Protection Regulation. governs how businesses collect, store, and process personal data from EU residents. If your product has EU users, EU-based customers, or EU employees, it applies to you regardless of where your company is headquartered.
The regulation requires specific things from you: documented policies, accurate records of data processing activities, a tested breach response plan, and evidence that your team actually follows through.
Decrypt Compliance assess your organization across the areas GDPR cares about most, document what we find, and issue a report you can share with customers, partners, or anyone who asks.
A lot of vendors will help you build policies and call you GDPR-ready. That’s not the same as an independent attestation from a qualified CPA firm. Decrypt Compliance is AICPA-accredited with a peer-reviewed audit practice.
Raymond Cheng and the Decrypt Compliance team trained at EY, PwC, and Deloitte before building this firm. The methodological rigor carries over. What doesn’t is the churn, the junior staff rotating through your engagement, and the account team that doesn’t know your product.
Our Reviews

Co-Founder Brick Towers AG
Expectation for an expected timeline was given and also adhered to which helped us a lot to manage expectations with our prospects. Decrypt accommodated our additional input to the draft audit report which helped us to stand out.

CEO, Tillion.ai

CEO, Leen Inc

CEO · jumbomail.me

Mid-Market

Small Business

Small Business · France
Learn from the experts


Not officially. No formal certification exists under GDPR the way it does for SOC 2 or ISO 27001. What Decrypt provides is an independent attestation report - a third-party document that reviews your data privacy controls against GDPR requirements. Most enterprise buyers and procurement teams accept this as sufficient evidence of compliance.
We look at four areas: how you conduct Data Protection Impact Assessments (DPIAs), how your privacy policies are documented and whether your team understands them, how you maintain records of data processing activities, and how prepared you are to respond to a breach. We then issue a report documenting findings across all four.
GDPR is the EU's data protection regulation. It applies to any organization that processes personal data from EU residents, regardless of where your company is based. If you have EU users, EU-based customers, or EU employees, you're in scope. The reach is broader than most companies assume.
Yes. We scope engagements to cover all three when needed. If you're selling into the EU, Canada, and the UK, we address those frameworks together rather than treating them as separate projects.
Most engagements run four to eight weeks from kickoff to final report, depending on where you're starting and how complex your data environment is. We'll give you a realistic timeline after an initial scoping call.
Yes, meaningfully so. Access management, incident response, and vendor risk management overlap across both frameworks. We identify what applies before we start so your team isn't duplicating documentation they've already produced.
That's the typical situation. Most of our clients are lean SaaS teams without dedicated compliance staff. We structure the engagement around your actual capacity and walk your team through what needs to be documented - you don't need to have it figured out before you call us.
No. A lot of companies come to us at the start of their GDPR process, not the end. The first call is a scoping conversation - it tells us where you are and gives you a clear picture of what the path forward looks like.
Get Started
Tell us about your company and we’ll get back to you with a clear path to certification – including timeline and pricing.
decrypt.cpa uses cookies for site functionality, usage analytics, and marketing attribution. Manage your preferences below — your choice applies across the site and you can change it any time. See our Cookie Policy for details.